WordPress Hacked With Spam Links? How to Find and Remove Them
Short answer: If your WordPress site was hacked with spam links, back it up as it is, lock it down, then check five places yourself: posts and settings in the database, admin users, core files, plugin and theme files, and the uploads folder plus .htaccess. A security plugin helps, but a clean scan is not proof. When we planted six fake spam items on a sandbox site, free wp-cli commands plus two basic shell commands found all six. The best free plugin we could run without an account found three.
Below: how spam link hacks work, the signs, what each free tool caught on our test site, a step-by-step cleanup, and how to stop it happening again.
Quick Facts
| Item | Details |
|---|---|
| What it is | Attackers add hidden links, spam pages or redirects to your site to borrow its search rankings |
| How common | Sucuri found SEO spam on 20.3% of the infected sites it cleaned in 2023, and in 38.3% of the hacked databases |
| Most common type | Japanese keyword spam, found on about 10% of sites Sucuri cleaned in 2023 |
| Where spam hides | Posts and revisions, the options table, fake admin users, core files, plugin and theme files, PHP files in uploads, .htaccess |
| Free tools that found everything on our test site | wp core verify-checksums, wp plugin verify-checksums --all, wp user list, wp db search, plus find and grep |
| Free plugins we ran | Quttera 4.1.0.41 (found 3 of 6), Sucuri Security 2.8 (1 of 6), Shield Security 22.2.3 (1 of 6), Anti-Malware Security 4.23.90 without a key (0 of 6) |
| Wordfence free | Version 9.0.2 would not scan until we registered for a free license, so it is not in the results |
| Google review after cleanup | A few days to a few weeks, according to Google |
| Main cause | Vulnerable plugins: Patchstack says 91% of the 11,334 new WordPress vulnerabilities found in 2025 were in plugins |
What a Spam Link Hack Looks Like
A spam link hack (also called spam link injection or SEO spam) is content added to your site without your permission to boost someone else’s search rankings. Links from your trusted domain to a pill shop or casino are worth money to a spammer, and so are thousands of spam pages hosted on your domain.
Common forms:
- Hidden link injection. Links added to posts, widgets or theme files and hidden with CSS such as
display:none. Visitors do not see them; search engines do. - The pharma hack. Drug names and links show up in your search results or page titles.
- The Japanese keyword hack. Thousands of auto-generated Japanese pages appear under your domain, usually selling knock-off goods. Sucuri says it has been one of the most common SEO spam infections for over nine years.
- Doorway pages. Spam pages that exist only to rank. Sucuri classed 53.5% of the SEO spam infections it saw in 2023 as doorways.
- Cloaked redirects. Visitors arriving from Google, or on a phone, get sent to a spam site, while you see a normal site. Sucuri put 28.19% of 2023 SEO spam in this group.
Google can then label your pages as hacked, drop them, or warn visitors away. Your own search rankings suffer while the spammer gets higher SEO authority out of your domain.
Signs Your WordPress Site Was Hacked
You usually cannot see spam link injections by browsing your own site. Check these instead:
- Search Console’s Security Issues report (under Security and Manual Actions). Google lists findings such as “Hacked: Content injection” with sample URLs.
- A
site:yourdomain.comGoogle search. Spam pages, Japanese titles or drug names in the results are a strong sign. - New Search Console owners. Google’s guide to the Japanese keyword hack notes that attackers often verify themselves as owners. Check Settings, then Users and permissions.
- The URL Inspection tool. It shows the page as Googlebot saw it, which exposes spam cloaked for search engines.
- Hidden links in the page source. Search the source for
display:none,visibility:hiddenor domains you do not know. - Admin users you did not create.
- Redirects only some visitors get. Test with
curl -I -e "https://www.google.com/" https://yourdomain.com/. A 301 or 302 to another domain is a red flag.
Our Test: Planting Fake Spam on a Sandbox Site
To see what free tools actually catch, we set up a fresh WordPress 7.1.2 test install on our own computer (a small fake bakery site with six posts) and planted six harmless, clearly labeled test items. No real malware was used: every link pointed to made-up .test domains, and every item carried a comment saying it was test data.
| # | Planted item | Where it lives | What it copies |
|---|---|---|---|
| 1 | Three links in a hidden display:none block inside a post |
Database (post and revision) | Hidden link injection |
| 2 | A fake administrator, wp_support_test, inserted straight into the database |
Database (users table) | Backdoor admin |
| 3 | A small PHP file that prints a hidden link | wp-content/uploads/ |
Dropped file |
| 4 | An extra PHP file that prints a hidden link | wp-includes/ |
Rogue core file |
| 5 | Three lines added to Hello Dolly that print a hidden footer link | wp-content/plugins/ |
Edited plugin |
| 6 | A rule sending visitors from Google, Bing or Yahoo to another domain | .htaccess |
Cloaked redirect |
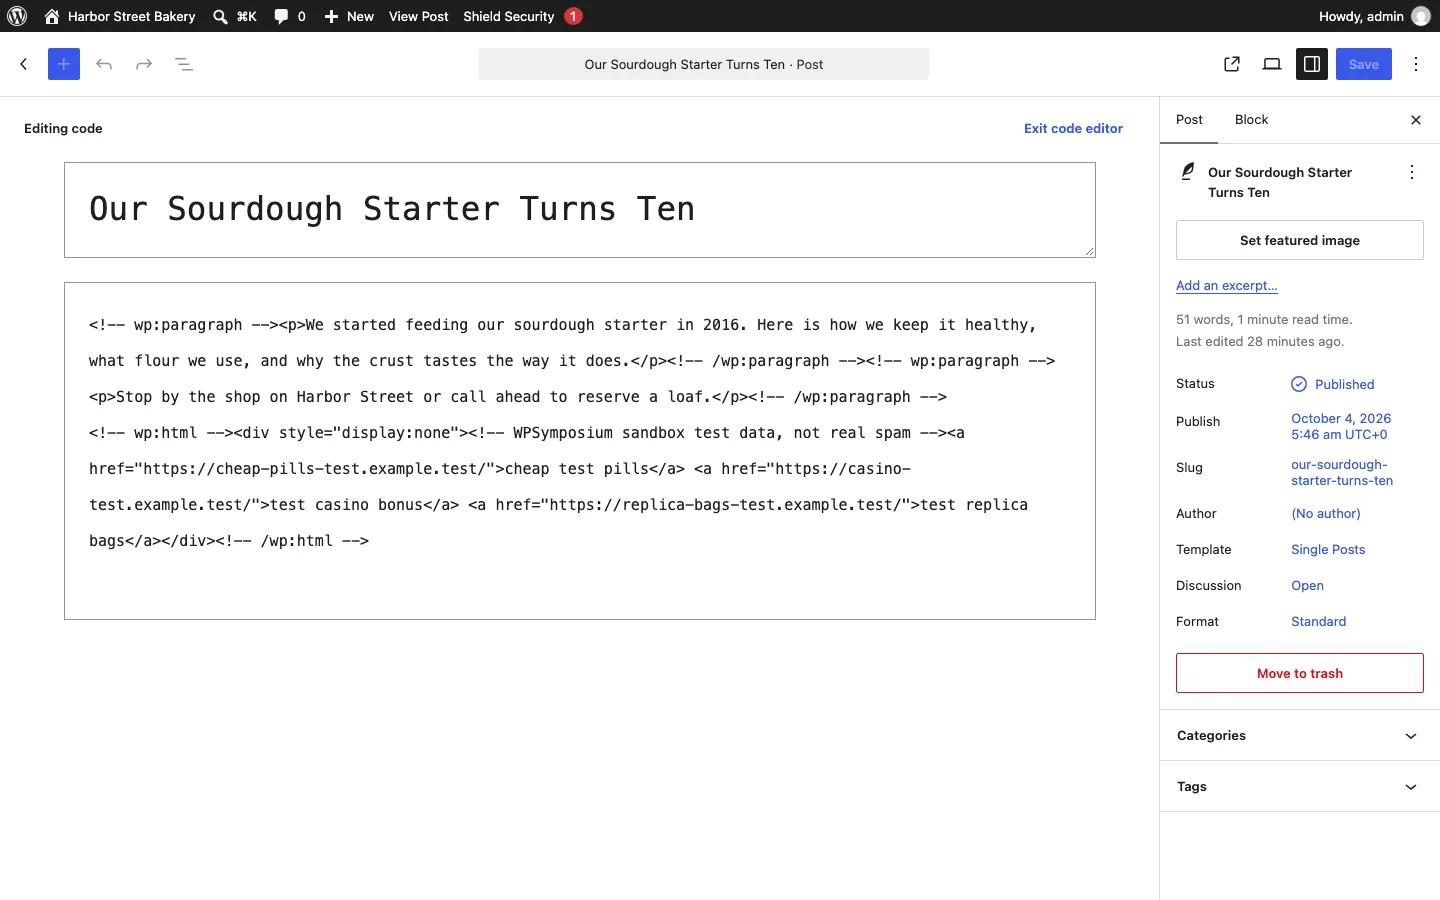
The planted hidden links in a test post, seen in the block editor’s code view on our WordPress 7.1.2 sandbox, October 2026.
In the normal visual editor, the post looked completely clean. The hidden block only showed in the code editor and the page source. A direct visit loaded normally, while a request with a Google referrer got a 302 redirect to the fake spam domain.
Which Tools Found What
| Planted item | wp-cli and shell | Sucuri Security 2.8 | Shield Security 22.2.3 | Quttera 4.1.0.41 | Anti-Malware 4.23.90 (no key) |
|---|---|---|---|---|---|
| 1. Hidden links in a post | Found (wp db search) |
Missed | Missed | Missed | Missed |
| 2. Fake admin user | Found (wp user list) |
Listed, not flagged | Not flagged | Listed, not flagged | Missed |
| 3. PHP file in uploads | Found (find) |
Missed | Missed | Missed | Missed |
| 4. Extra file in wp-includes | Found (wp core verify-checksums) |
Found | Found | Found | Missed |
| 5. Edited plugin file | Found (wp plugin verify-checksums) |
Missed | Pro only | Found | Missed |
6. .htaccess redirect |
Found (grep) |
Missed | Missed | Found | Missed |
| False alarms | 1 (a file from our Docker setup) | 1 (same file) | 0 | 1 (a library file inside Shield) | 11 normal files |
wp-cli: the most reliable free option
wp-cli is the official command-line tool for WordPress, and many hosts include it over SSH. On our test site, four wp-cli commands plus find and grep found every planted item.
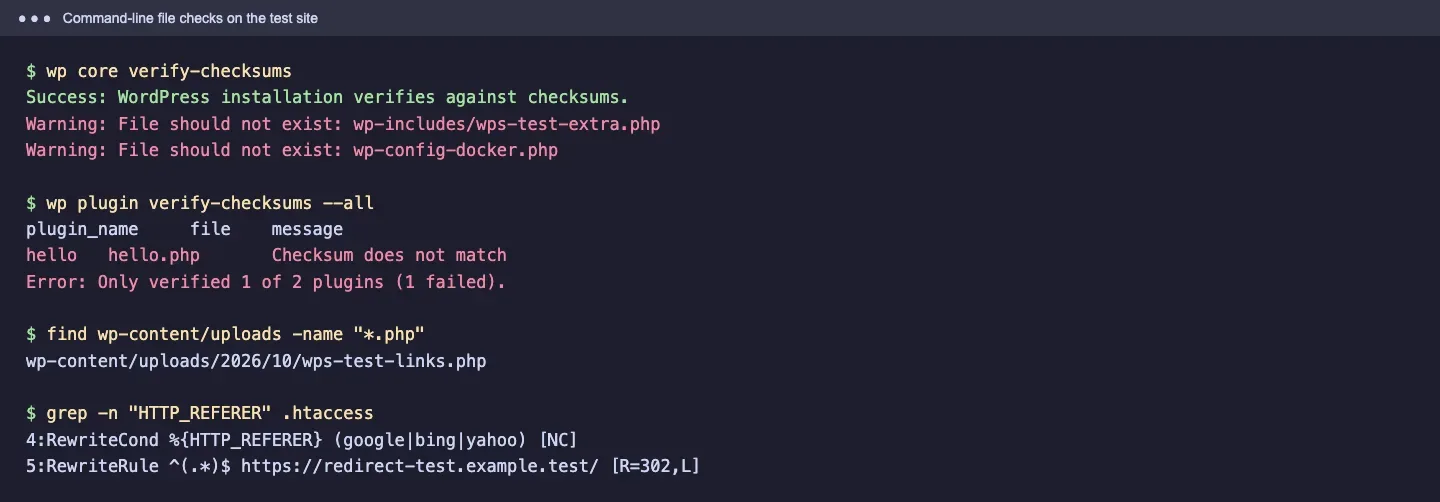
File checks on the test site: core and plugin checksums, PHP files in uploads, and the .htaccess redirect, October 2026.
wp core verify-checksumscompares core files with the official WordPress.org copies. It still prints “Success” while also warning that a file “should not exist”, so read the warnings.wp plugin verify-checksums --allcaught the edited Hello Dolly file. It only covers WordPress.org plugins, so paid plugins need a fresh copy from the vendor.- Neither command checks uploads or
.htaccess, which is whyfindandgrepare part of the routine. Uploads folders should hold images and documents, not PHP files (a few plugins, such as Sucuri, keep their own data files there).
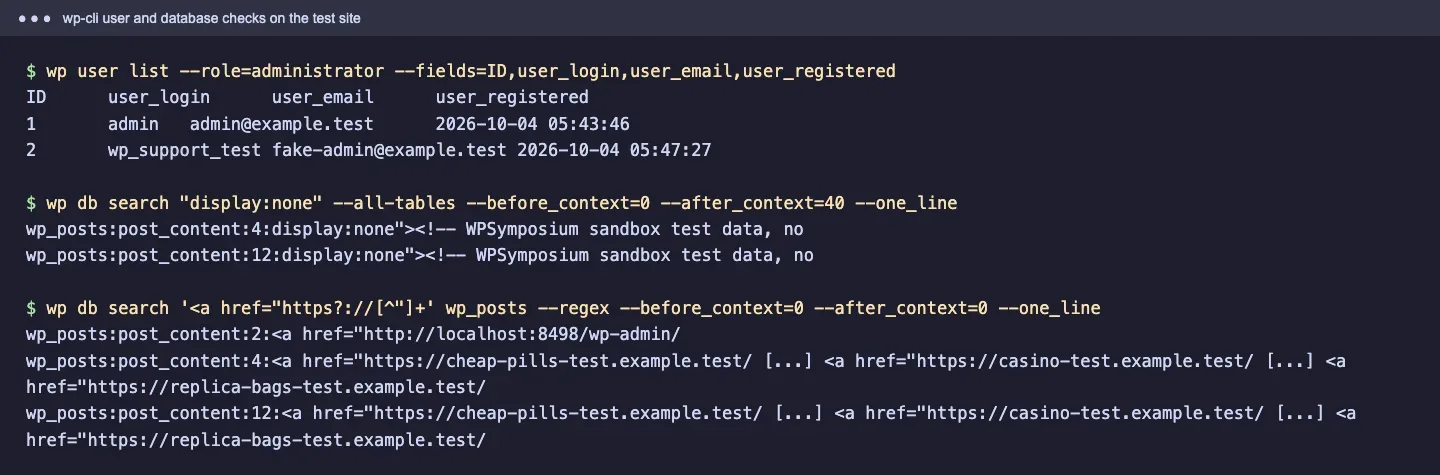
wp user list and wp db search on the test site, showing the fake admin and the hidden links in both the post and its revision, October 2026.
The database search showed a detail that is easy to miss: the links were in the post (ID 4) and in an older revision of it (ID 12). Edit only the post and the spam survives in revisions.
Sucuri Security (free)
Sucuri’s WordPress Integrity check compares core files with WordPress.org. It flagged the extra wp-includes file straight away, with options to mark, restore or delete it.
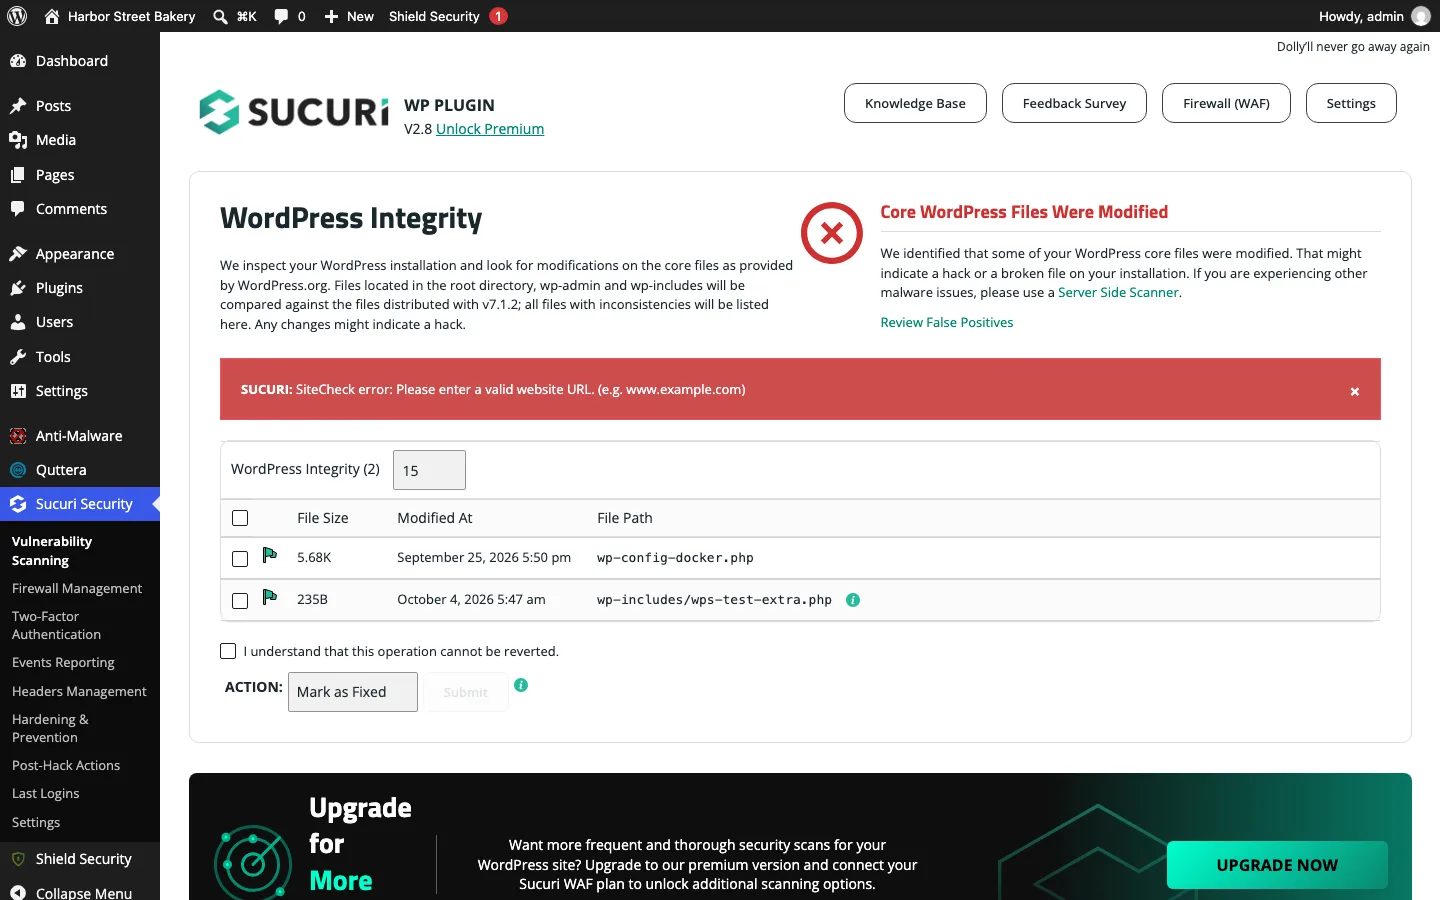
Sucuri Security 2.8’s integrity check on the test site, flagging the planted file in wp-includes, October 2026.
The check only covers core folders, so it missed everything else. Sucuri’s malware scan is SiteCheck, a remote scanner of your public pages, and it cannot reach a local test site. On a live site it may spot hidden links in your HTML, so treat this as a gap in our test rather than a verdict on SiteCheck. The Post-Hack Actions page is handy for cleanup: it resets secret keys, resets user passwords and reinstalls free plugins.
Shield Security (free)
The free version of Shield scans WordPress core files only. It flagged the extra wp-includes file as “Unrecognised”. Plugin and theme scanning, PHP malware scanning and vulnerability scanning all showed “Upgrade Required”.
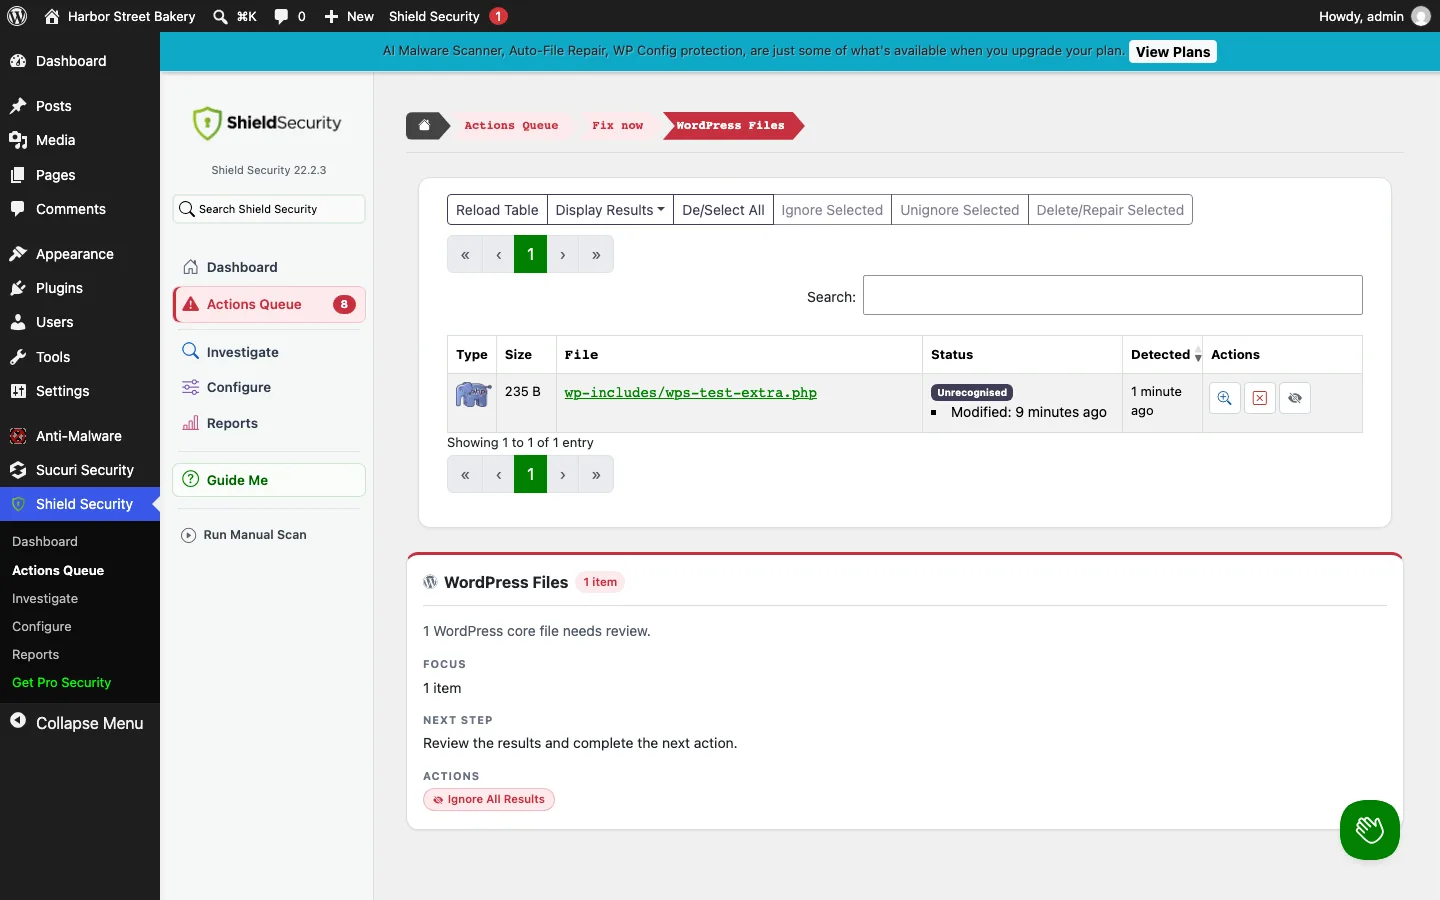
Shield Security 22.2.3’s free core file scan on the test site, October 2026.
After the cleanup, wp plugin verify-checksums reported “File was added” inside Shield’s own folder, because Shield writes a small flag file there. It is a harmless false alarm, and a reminder to read results rather than count them.
Quttera ThreatSign (free)
Quttera’s free server-side scan checked 9,780 files and 2,369 database rows, and did best of the plugins. It flagged the .htaccess redirect as malicious and the extra core file and edited Hello Dolly file as suspicious. It missed the database links and the uploads file, and its Admin Users tab listed the fake admin without raising an alarm. It also called a normal library file inside Shield a “backdoor”.
It was rough on WordPress 7.1.2: its pages printed PHP deprecation notices, and the scan page froze our browser more than once, so we read the final results from the plugin’s own status calls.
Anti-Malware Security, Wordfence and MalCare
Anti-Malware Security (GOTMLS) needs a free key from its developer before it downloads malware definitions. Without one, only its “Potential Threats” check runs. On our test site it took 49 seconds, listed 11 normal files (including wp-config.php) and missed all six planted items.
Wordfence has over 5 million active installs on WordPress.org as of October 2026, the most of any plugin here. Its listing says the free scanner checks for malware, backdoors, SEO spam, malicious redirects and code injections, with signatures delayed 30 days compared with Premium. But version 9.0.2 would not start a scan until we registered an email address for a free license, and we did not create an account.
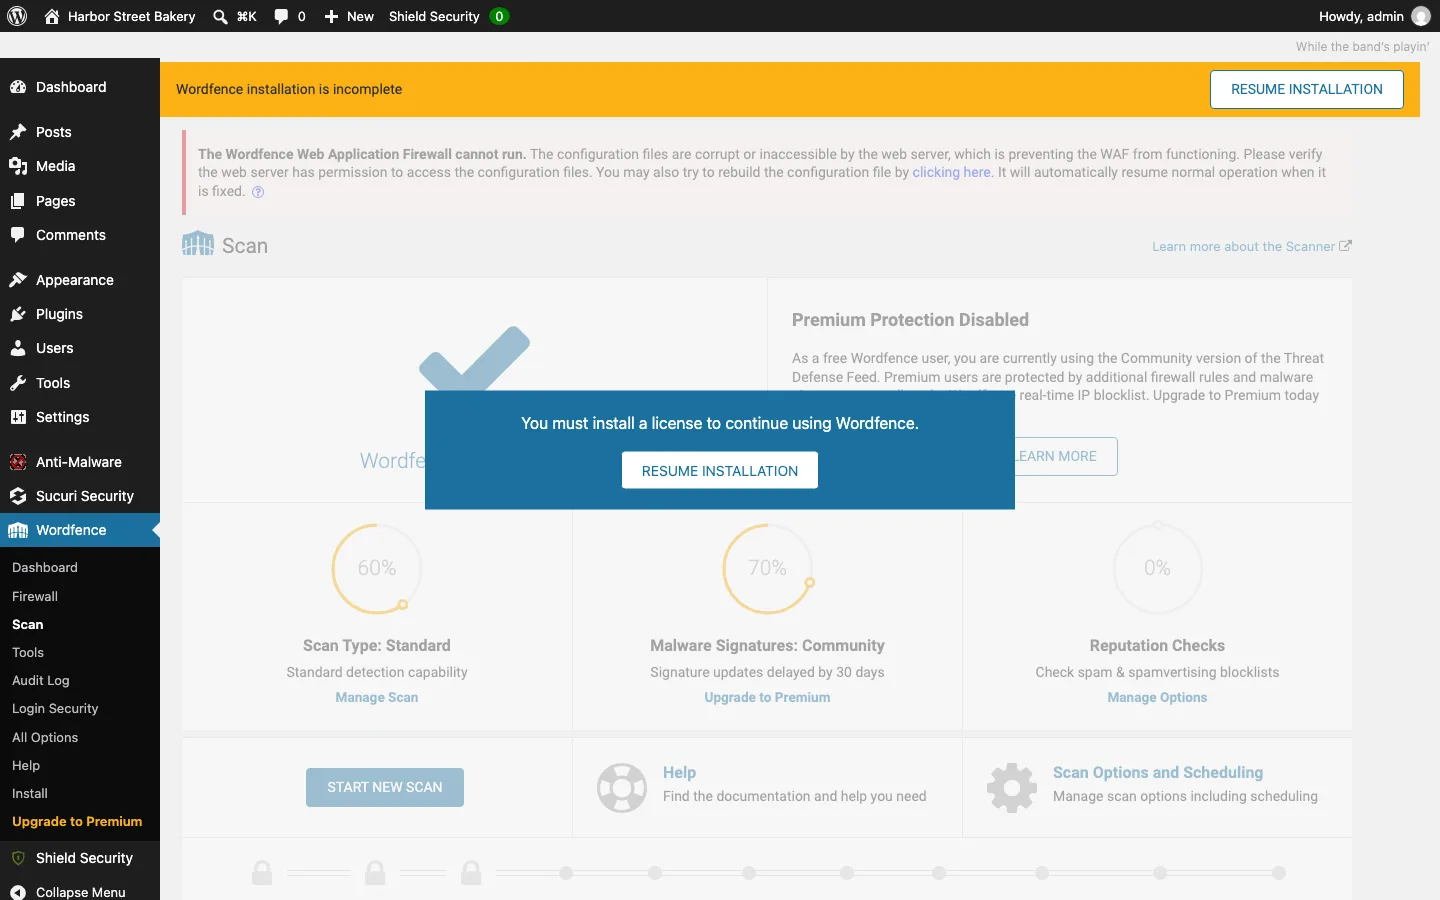
Wordfence 9.0.2 on the test site, asking for a license before it will scan, October 2026.
MalCare also needs an account: its WordPress.org listing says scanning runs on MalCare’s servers.
How to Clean a WordPress Site Hacked With Spam Links
These are the steps we recommend, and the ones we used to clean the test site. The commands assume SSH with wp-cli. With only cPanel, the same checks work through File Manager and phpMyAdmin, just more slowly.
1. Back up the hacked site first
Copy the files and database before changing anything, and store the copy outside the web root.
wp db export backup-hacked.sql
tar czf site-files-hacked.tgz .
Label it as infected. A backup from before the hack is your fastest way back, if you know when the hack happened. See our WordPress backup plugin comparison, where we restored a broken test site with six free plugins.
2. Put the site in maintenance mode
wp maintenance-mode activate keeps visitors and Google away from spam pages while you work.
3. Remove unknown admins and change every password
Delete accounts you do not recognize and reassign their content, for example wp user delete 2 --reassign=1. Then change passwords for every admin, your hosting account, SFTP and the database user, and remove unknown Search Console owners.
4. Reset your secret keys
wp config shuffle-salts replaces the keys in wp-config.php that sign login cookies, which logs everyone out, including an attacker with a stolen session. Sucuri’s Post-Hack Actions page does the same, or you can edit your wp-config.php file by hand.
5. Search the database yourself
wp db search "display:none" --all-tables
wp db search "visibility:hidden" --all-tables
wp db search '<a href="https?://[^"]+' wp_posts --regex --one_line
Clean each infected post in the code editor, then delete old revisions that still hold the spam (wp post list --post_type=revision --post_parent=<ID> lists them). Check wp_options too, especially widget and theme settings.
6. Replace core files
Run wp core verify-checksums, then wp core download --force --skip-content --version=<your version> to overwrite every core file with a clean copy. This does not delete extra files, so remove anything reported as “should not exist” unless you know what it is.
7. Reinstall plugins and themes
Delete any plugin that fails wp plugin verify-checksums --all and install a fresh copy, from WordPress.org or the vendor. Do the same for your theme. Delete what you do not use, and never reinstall nulled (pirated) copies.
8. Remove unknown files and fix .htaccess
find wp-content/uploads -name "*.php"
find . -name "*.php" -mtime -30
Delete PHP files in uploads that no plugin of yours needs. The second command lists PHP files changed in the last 30 days. In .htaccess, remove rules you did not add, especially ones that check HTTP_REFERER or HTTP_USER_AGENT and redirect elsewhere. The block between # BEGIN WordPress and # END WordPress is normal.
9. Check again, then reopen the site
Re-run every check. On our test site, the cleanup took a few minutes once we knew where each item was, and the second run came back clean apart from the two known false alarms.
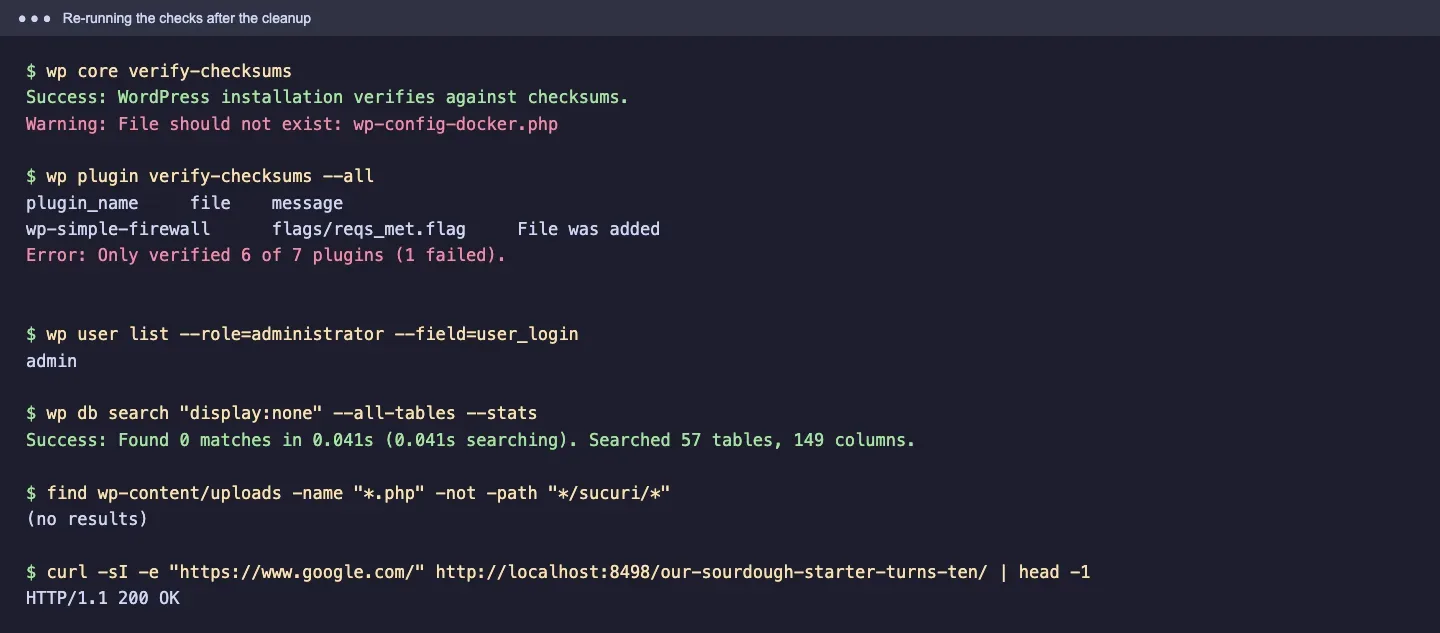
The same checks after the cleanup on our test site, October 2026.
Then run wp maintenance-mode deactivate and open your site from a Google result on your phone.
10. Ask Google to review the site
Fix every issue listed in Search Console on every page, then click Request Review in the Security Issues report and describe your fixes. Google says a review takes from a few days to a few weeks, and asks you not to resubmit before you get a decision. The Removals tool can hide already-indexed spam pages while Google recrawls.
If the spam keeps coming back, a backdoor or unpatched hole is still there. Our full WordPress malware removal guide covers other hiding places, such as must-use plugins and cron jobs, and compares paid cleanup prices, which are often cheaper than more hours of searching.
How to Stop It Happening Again
Most hacks come through known holes in plugins. Patchstack’s State of WordPress Security in 2026 report counted 11,334 new vulnerabilities in 2025, up 42% from 2024: 91% in plugins, 9% in themes and only 6 in core. It found 46% had no fix from the developer by the time they were made public. Sucuri found 39.1% of the CMS installs it cleaned in 2023 were out of date when infected.
For your WordPress install:
- Update core quickly. If you worry an update will break something, try it on a staging copy of your site first.
- Use strong, unique passwords and two-factor login for every admin, and keep admin accounts to a minimum.
- Check your administrator list every month.
- Disable the dashboard file editor with
define( 'DISALLOW_FILE_EDIT', true );inwp-config.php. - Block PHP in uploads. Sucuri’s Hardening page or your host can do this.
- Keep off-site backups. All-in-One WP Migration can also move a clean copy to a new server.
For plugins and themes: update your plugins and themes as soon as security fixes ship, delete anything inactive, and install only from WordPress.org or the original vendor.
For hosting: good hosts isolate sites, keep server software current and often include malware scanning. If you are on bare-bones shared hosting, managed WordPress hosting takes part of this job off your plate.
Run the checksum and user checks once a month, and turn on Search Console email alerts so Google tells you about security issues as soon as it finds them.
FAQ
How do I know if my WordPress site has been hacked?
Look for a warning in Search Console’s Security Issues report, spam pages in a site:yourdomain.com search, admin users you did not create, links hidden with display:none in your page source, and redirects that only happen from Google or on a phone. Many spam hacks are invisible when you browse your own site.
Can a security plugin remove spam links for me?
Partly. On our test site, the best free plugin we could run without an account (Quttera) found three of six planted items, and Sucuri and Shield found one each. None found the hidden links in the post. Paid plans and cleanup services do more, but confirm the result with your own checks.
What is the Japanese keyword hack?
A hack that creates thousands of auto-generated Japanese pages on your domain, usually selling knock-off goods. A site: search reveals it. Sucuri says it was the most common SEO spam it cleaned in 2023, found on about 10% of the sites it fixed. Also remove any Search Console owners the attacker added.
Why does my site redirect to spam only from Google or on mobile?
Attackers add rules in .htaccess, a plugin file or the database that only redirect visitors from a search engine or on a phone, so you see a normal site. On our test site, a referrer-based .htaccess redirect was found by grep and Quttera and missed by the other plugins.
How long does it take Google to remove the hacked site warning?
Google says a review takes from a few days to a few weeks after you click Request Review. Fix every listed issue first, since a request sent too early can slow down the next one.